The Smart-Driving Lockout Exposes Trust Gaps
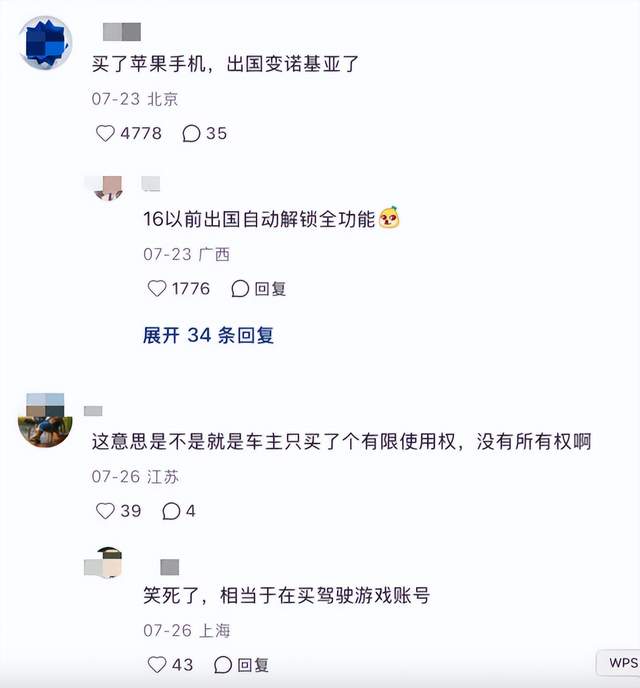
A vehicle lockout shows why AI safety includes governance, not just better perception models.
30-Second TL;DR
What Changed
A cross-border vehicle lockout raises concerns about remote control over connected cars.
Why It Matters
Such incidents can undermine user trust in connected vehicles and expose the governance risks of remotely managed AI systems. For AI companies, the lesson extends to access controls, geographic restrictions, incident recovery, and transparent user communication.
What To Do Next
Add an offline recovery and manual-override test to your autonomous-vehicle safety suite, covering border changes, connectivity loss, and disputed remote commands.
Key Points
- •A cross-border vehicle lockout raises concerns about remote control over connected cars.
- •Technical maturity alone is insufficient for trustworthy smart-driving products.
- •Rules, accountability, and user-rights protections must evolve alongside autonomous-driving functions.
Deep Insight
AI-generated analysis for this event — not the original article.
Enhanced Key Takeaways
- •The incident highlights the vulnerability of Over-the-Air (OTA) update protocols, where remote server-side commands can override local vehicle control systems regardless of the driver's physical presence.
- •Geofencing technologies used by manufacturers to restrict vehicle operation in specific regions are increasingly being criticized for lacking transparency and failing to provide 'emergency override' mechanisms for users.
- •Legal experts are pointing to a lack of standardized 'digital sovereignty' laws for connected vehicles, which currently allow manufacturers to unilaterally disable vehicle functions based on proprietary terms of service.
- •Data privacy regulations in cross-border scenarios remain fragmented, creating a 'gray zone' where vehicle telemetry data may be subject to conflicting jurisdictional requirements, complicating remote lockout justifications.
- •Industry analysts note that the 'kill switch' capability, while intended for anti-theft or safety compliance, is being repurposed by OEMs for commercial enforcement, leading to a breakdown in consumer trust.
Technical Deep Dive
- Remote lockout mechanisms typically rely on a Telematics Control Unit (TCU) that maintains a persistent connection to the OEM's cloud backend via 4G/5G networks.
- The lockout command is often executed by sending a specific CAN bus message (Controller Area Network) that instructs the Gateway module to disable the ignition or immobilize the powertrain.
- Authentication for these remote commands frequently uses asymmetric encryption (PKI), but the vulnerability often lies in the server-side authorization logic rather than the encryption itself.
- Many modern smart vehicles utilize a 'Heartbeat' signal between the vehicle and the cloud; if the vehicle fails to report its location within a geofenced boundary, the cloud can trigger a 'limp mode' or total lockout.
Future ImplicationsAI analysis grounded in cited sources
Timeline
- 2024-05Initial industry reports emerge regarding remote geofencing restrictions in cross-border vehicle exports.
- 2025-02Regulatory bodies begin investigating the safety implications of remote vehicle immobilization features.
- 2026-06Public controversy peaks following a high-profile cross-border lockout incident involving a major smart-driving EV brand.
Weekly AI Recap
Read this week's curated digest of top AI events →
AI-curated news aggregator. All content rights belong to original publishers.
Original source: 钛媒体 ↗
This is a summary, not the original. Read the source, or get the weekly briefing.
The weekly digest
One email a week. Unsubscribe anytime.