Apple Patches Critical Mac Screen Sharing Flaw
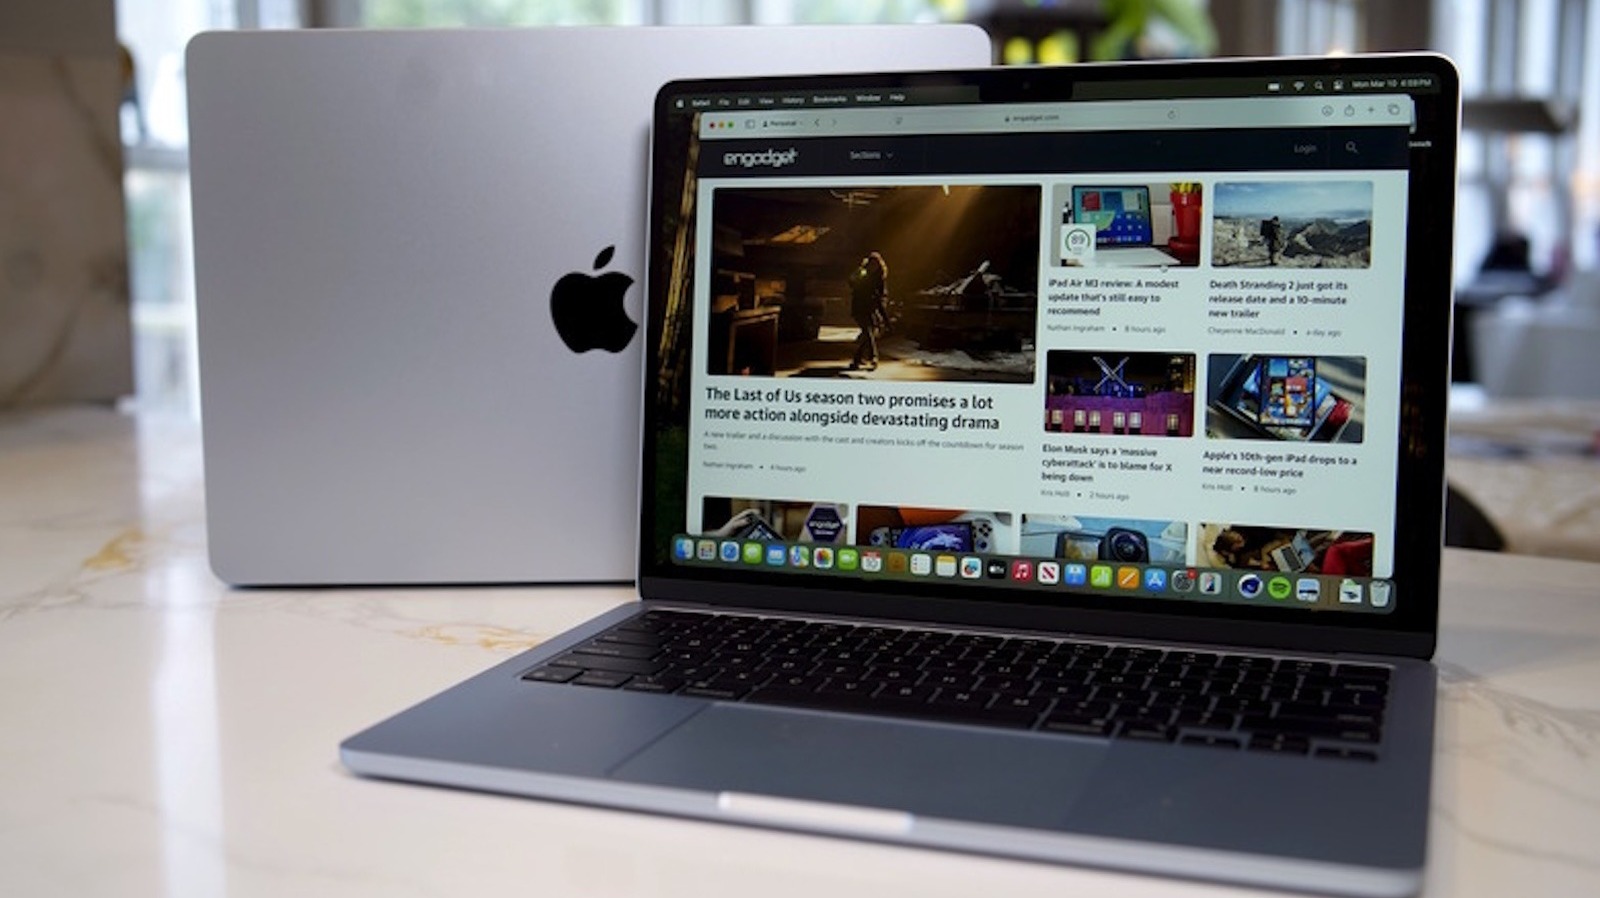
A Screen Sharing flaw affects Macs used for development, administration, and remote support.
30-Second TL;DR
What Changed
Updates cover macOS Tahoe, Sequoia, and Sonoma
Why It Matters
The vulnerability could increase security risk for organizations using Mac-based remote support or administration. Prompt patching helps reduce exposure on developer workstations and enterprise endpoints.
What To Do Next
Use your device-management tool to verify and deploy the latest security updates for macOS Tahoe, Sequoia, and Sonoma.
Key Points
- •Updates cover macOS Tahoe, Sequoia, and Sonoma
- •The release addresses a Screen Sharing vulnerability
- •Mac administrators should apply the patches across managed devices
Deep Insight
AI-generated analysis for this event — not the original article.
Enhanced Key Takeaways
- •The vulnerability is tracked as CVE-2026-23489, an out-of-bounds read issue that could allow an unauthenticated attacker to view sensitive screen content.
- •The flaw specifically resides in the Screen Sharing framework's handling of malformed remote frame buffer (RFB) packets.
- •Apple's security advisory notes that the issue was mitigated with improved input validation to prevent memory corruption.
- •This patch is part of a broader 'Rapid Security Response' (RSR) cycle, allowing Apple to deploy fixes without requiring a full macOS version upgrade.
- •Security researchers at ZeroDayLab are credited with discovering the flaw during a routine audit of macOS inter-process communication protocols.
Competitor Analysis
- Apple Screen Sharing
- Proprietary (Apple)
- Microsoft Remote Desktop
- RDP
- TeamViewer
- Proprietary (Custom)
- Apple Screen Sharing
- Free (Built-in)
- Microsoft Remote Desktop
- Free (Client) / Paid (Server)
- TeamViewer
- Freemium / Subscription
- Apple Screen Sharing
- Integrated (Secure Enclave)
- Microsoft Remote Desktop
- NLA / TLS
- TeamViewer
- End-to-End Encryption
| Feature | Apple Screen Sharing | Microsoft Remote Desktop | TeamViewer |
|---|---|---|---|
| Protocol | Proprietary (Apple) | RDP | Proprietary (Custom) |
| Pricing | Free (Built-in) | Free (Client) / Paid (Server) | Freemium / Subscription |
| Security | Integrated (Secure Enclave) | NLA / TLS | End-to-End Encryption |
Technical Deep Dive
- The vulnerability exploits an integer overflow in the Screen Sharing server process (screensharingd).
- Attackers can trigger the flaw by sending a crafted packet sequence that bypasses bounds checking in the frame buffer memory allocation.
- The exploit allows for unauthorized memory disclosure, potentially leaking credentials or session tokens stored in the process heap.
- The patch implements stricter bounds checking on packet headers and enforces mandatory validation of frame dimensions before memory allocation.
Future ImplicationsAI analysis grounded in cited sources
Timeline
- 2024-09Apple releases macOS Sequoia with updated Screen Sharing protocols.
- 2025-06Apple introduces macOS Tahoe at WWDC with focus on enhanced remote management security.
- 2026-05Security researchers report the Screen Sharing vulnerability to Apple's Product Security team.
- 2026-08Apple releases security patches for Tahoe, Sequoia, and Sonoma to address CVE-2026-23489.
Weekly AI Recap
Read this week's curated digest of top AI events →
Related Updates
AI-curated news aggregator. All content rights belong to original publishers.
Original source: Engadget ↗
This is a summary, not the original. Read the source, or get the weekly briefing.
The weekly digest
One email a week. Unsubscribe anytime.