Meta Bolsters E2E Encrypted Backups
Meta's HSM vault secures backups from insiders—vital for AI data privacy infra
30-Second TL;DR
What Changed
HSM-based Backup Key Vault enables E2E encrypted chat backups
Why It Matters
Enhances user privacy and trust in Meta's messaging platforms by preventing company access to backups. Sets a higher security standard for cloud-backed consumer apps, potentially influencing competitors.
What To Do Next
Study Meta's HSM Backup Key Vault for secure key management in AI data backup pipelines.
Key Points
- •HSM-based Backup Key Vault enables E2E encrypted chat backups
- •Recovery codes secured in tamper-resistant HSMs
- •Inaccessible to Meta staff and cloud storage providers
- •Protects WhatsApp and Messenger message histories
Deep Insight
AI-generated analysis for this event — not the original article.
Enhanced Key Takeaways
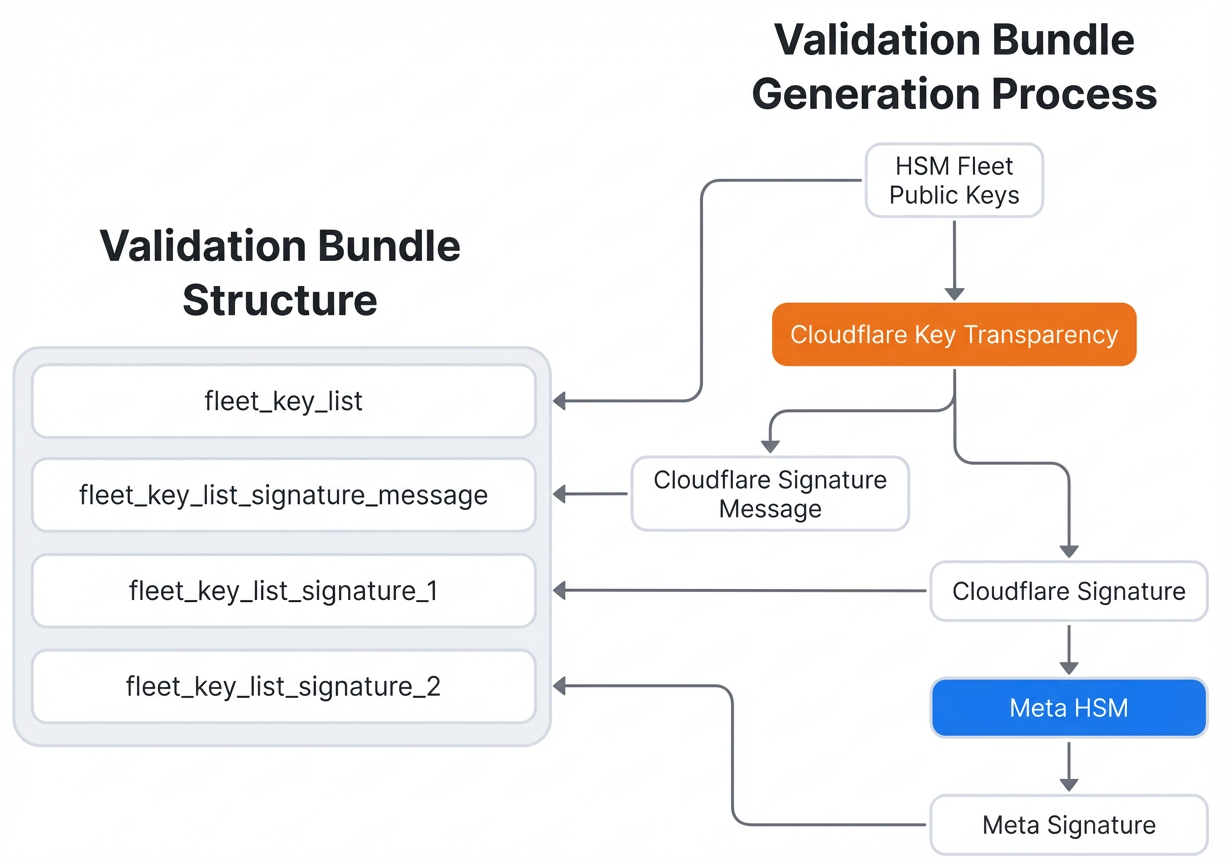
- •The system utilizes a 'Key Transparency' protocol, allowing users to cryptographically verify that their backup keys have not been tampered with or replaced by malicious actors.
- •Meta implemented a 'rate-limiting' mechanism on the HSMs to prevent brute-force attacks against user recovery codes, effectively mitigating the risk of unauthorized decryption attempts.
- •The architecture supports a 'secret sharing' scheme where the key is split into fragments, ensuring that no single component of the infrastructure holds the complete decryption key.
Competitor Analysis
- Meta (WhatsApp/Messenger)
- HSM-based Key Vault
- Signal
- Local-only or encrypted cloud
- Apple (iCloud Advanced Data Protection)
- End-to-end encrypted
- Meta (WhatsApp/Messenger)
- Managed HSM / User-held code
- Signal
- User-held passphrase
- Apple (iCloud Advanced Data Protection)
- User-held recovery key
- Meta (WhatsApp/Messenger)
- Meta-managed infrastructure
- Signal
- User-managed
- Apple (iCloud Advanced Data Protection)
- Apple-managed infrastructure
| Feature | Meta (WhatsApp/Messenger) | Signal | Apple (iCloud Advanced Data Protection) |
|---|---|---|---|
| Backup Encryption | HSM-based Key Vault | Local-only or encrypted cloud | End-to-end encrypted |
| Key Management | Managed HSM / User-held code | User-held passphrase | User-held recovery key |
| Access | Meta-managed infrastructure | User-managed | Apple-managed infrastructure |
Technical Deep Dive
- •Hardware Security Modules (HSMs) are FIPS 140-2 Level 3 compliant, ensuring physical tamper-resistance.
- •The key vault service uses a blind-signing protocol, meaning the HSM signs the key request without ever seeing the actual user data or the full recovery code.
- •Implementation relies on a combination of Elliptic Curve Diffie-Hellman (ECDH) for key exchange and AES-256-GCM for the actual encryption of the backup blobs.
- •The system integrates with the existing Signal Protocol implementation used by WhatsApp to ensure consistency in cryptographic primitives.
Future ImplicationsAI analysis grounded in cited sources
Timeline
- 2021-10Meta announces the rollout of end-to-end encrypted backups for WhatsApp.
- 2023-01Meta begins integrating E2E encryption by default for Messenger chats.
- 2024-05Meta upgrades the key management infrastructure to support hardware-backed security.
- 2026-05Meta launches the HSM-based Backup Key Vault for unified cross-platform support.
Weekly AI Recap
Read this week's curated digest of top AI events →
AI-curated news aggregator. All content rights belong to original publishers.
Original source: Meta Engineering Blog ↗
This is a summary, not the original. Read the source, or get the weekly briefing.
The weekly digest
One email a week. Unsubscribe anytime.