Cloudflare Accelerates Post-Quantum Security to 2029
Quantum attacks advance faster—Cloudflare's 2029 target secures AI cloud infra now.
30-Second TL;DR
What Changed
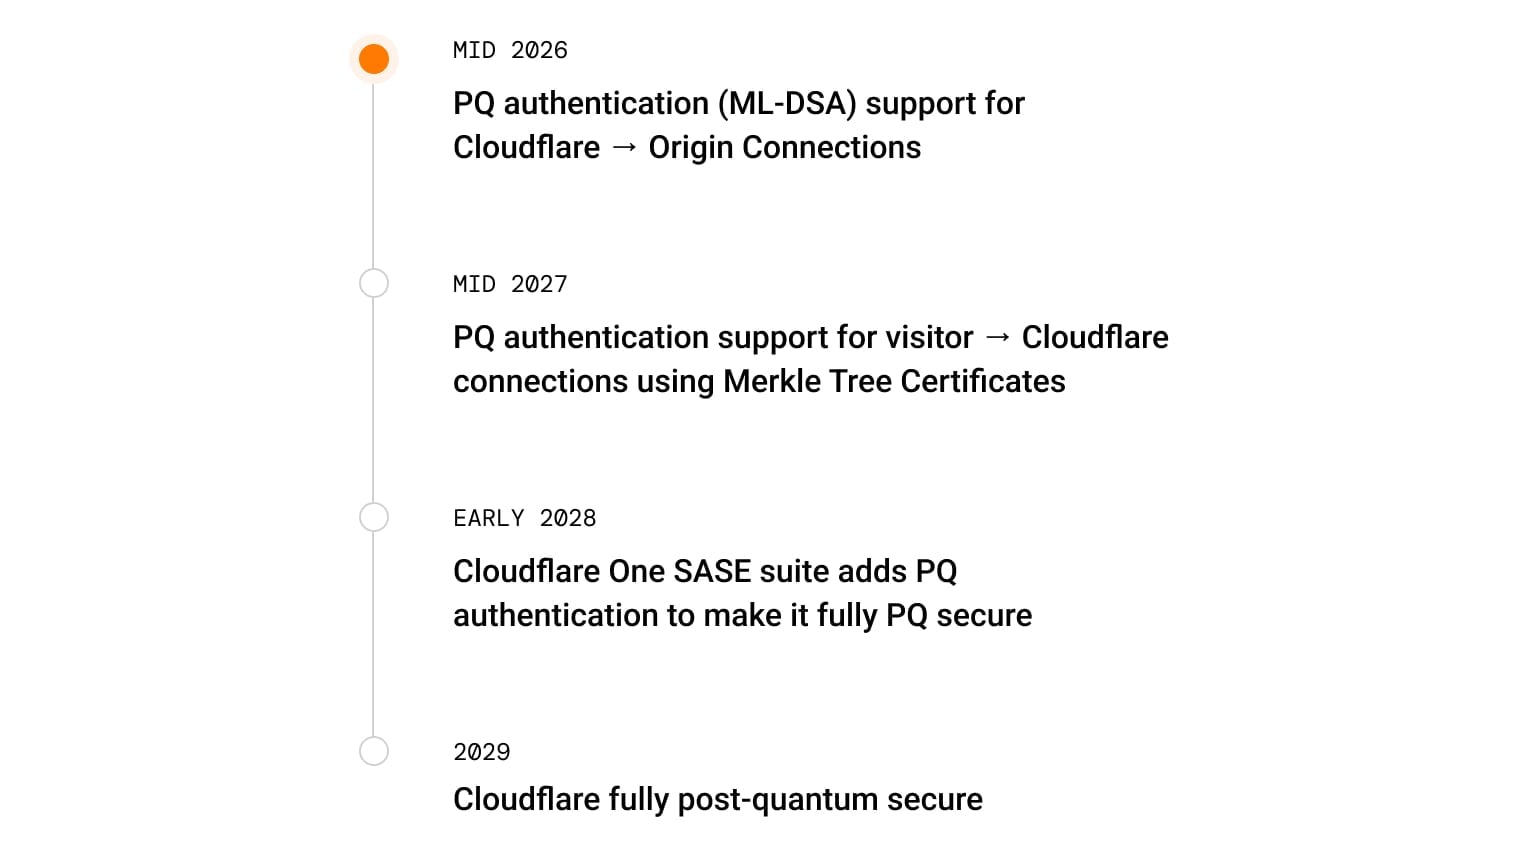
Cloudflare moves full post-quantum security target to 2029
Why It Matters
This timeline shift bolsters long-term security for cloud-based AI workloads against quantum threats. AI practitioners using Cloudflare services gain earlier protection for data encryption and APIs.
What To Do Next
Audit your Cloudflare deployments for post-quantum readiness using their security dashboard.
Key Points
- •Cloudflare moves full post-quantum security target to 2029
- •Driven by accelerated quantum hardware/software advances
- •Prepares for earlier-than-expected quantum attack threats
Deep Insight
AI-generated analysis for this event — not the original article.
Enhanced Key Takeaways
- •Cloudflare is prioritizing the deployment of Kyber (ML-KEM) and Dilithium (ML-DSA) algorithms, which were recently standardized by NIST to provide resistance against Shor's algorithm.
- •The 2029 target is specifically aligned with the 'Q-Day' threat model, where cryptographically relevant quantum computers (CRQCs) are projected to break current RSA and ECC encryption standards.
- •Cloudflare's strategy involves a hybrid key exchange approach, combining classical ECDH with post-quantum algorithms to ensure security against both current and future threats during the transition period.
Competitor Analysis
- Cloudflare
- Yes (Hybrid)
- Google (Cloud)
- Yes
- AWS
- Yes
- Microsoft (Azure)
- Yes
- Cloudflare
- Full (ML-KEM/DSA)
- Google (Cloud)
- Full
- AWS
- Full
- Microsoft (Azure)
- Full
- Cloudflare
- Yes (Magic WAN)
- Google (Cloud)
- No
- AWS
- No
- Microsoft (Azure)
- No
- Cloudflare
- Included in Tier
- Google (Cloud)
- Included in Tier
- AWS
- Included in Tier
- Microsoft (Azure)
- Included in Tier
| Feature | Cloudflare | Google (Cloud) | AWS | Microsoft (Azure) |
|---|---|---|---|---|
| PQ-Ready TLS | Yes (Hybrid) | Yes | Yes | Yes |
| NIST Standard Support | Full (ML-KEM/DSA) | Full | Full | Full |
| Public PQ VPN | Yes (Magic WAN) | No | No | No |
| Pricing | Included in Tier | Included in Tier | Included in Tier | Included in Tier |
Technical Deep Dive
- •Implementation of FIPS 203 (ML-KEM) for key encapsulation mechanisms to replace traditional Diffie-Hellman.
- •Utilization of FIPS 204 (ML-DSA) for digital signatures to secure certificate chains.
- •Deployment of hybrid key exchange protocols (e.g., X25519 + Kyber768) to maintain backward compatibility while providing quantum resistance.
- •Integration of post-quantum algorithms into the Cloudflare edge network via the BoringSSL library.
Future ImplicationsAI analysis grounded in cited sources
Timeline
- 2022-09Cloudflare launches support for Kyber in its edge network.
- 2023-07Cloudflare enables post-quantum key exchange for all customer websites by default.
- 2024-08Cloudflare integrates NIST-standardized ML-KEM and ML-DSA algorithms into its security stack.
Weekly AI Recap
Read this week's curated digest of top AI events →
Related Updates

AI-curated news aggregator. All content rights belong to original publishers.
Original source: Cloudflare Blog ↗
This is a summary, not the original. Read the source, or get the weekly briefing.
The weekly digest
One email a week. Unsubscribe anytime.